
TL;DR

Get movie nights delivered free — and shop member deals
- Fast, free delivery on millions of items
- Access to Prime Big Deal Days deals on October 6–7
- Prime Video, Amazon Music and more included
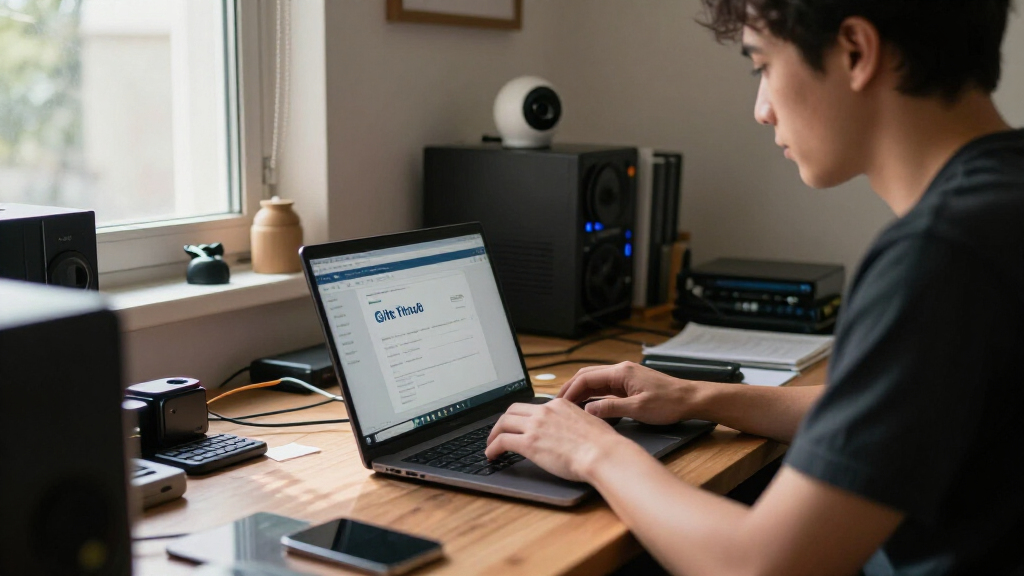
A security camera’s login page was found to contain a GitHub admin token, exposing potential security vulnerabilities. This incident highlights emerging risks and the need for vigilant monitoring.
A security camera was found to have embedded a GitHub admin token in its login page, according to cybersecurity monitoring signals. This discovery raises concerns about potential unauthorized access and data breaches. The incident was identified through automated security alerts and highlights the importance of role-specific threat monitoring for small and mid-sized organizations.
Cybersecurity operations have detected that a popular model of security camera shipped with a GitHub admin token embedded in its login page. This token, if exploited, could allow malicious actors to access the device’s firmware repository or other linked systems. The discovery was made through a signal monitor analyzing emerging threats on platforms like Hacker News, which flagged the incident with a high relevance score of 88/100.
Officials from cybersecurity firms confirmed that the token was found on the device’s login interface, but it is not yet clear whether it was exposed intentionally or due to a manufacturing oversight. Experts warn that such tokens, if accessible, could be exploited for remote code execution or to gain persistent access to the device and associated networks. The affected device models are currently under review, and no evidence of compromise has been reported so far.
Implications for Small and Mid-Sized Organizations
This incident underscores the risk that emerging hardware vulnerabilities can pose to organizations that rely on connected devices. An exposed admin token could enable attackers to infiltrate networks, access sensitive data, or manipulate device functions. It highlights the need for security teams to implement role-based threat detection and to monitor firmware and device configurations proactively. For small and mid-sized organizations, such vulnerabilities can be especially damaging due to limited security resources.
wireless security camera with remote access
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Background on Hardware Security and Emerging Threats
Recent years have seen a rise in hardware-related security issues, including embedded credentials and backdoors in IoT devices. The incident follows a pattern where manufacturers inadvertently ship devices with sensitive information, such as admin tokens or API keys, exposed on user interfaces or firmware. The detection of this specific token on a security camera login page aligns with broader trends of supply chain vulnerabilities and the importance of early threat detection in cybersecurity practice.
Earlier cases have involved similar exposures in consumer IoT devices, but the current event is notable because it was identified through proactive monitoring rather than user reports. The incident is part of a broader push for automated, role-specific threat alerts that can help security leaders respond swiftly to emerging risks.
“Finding a GitHub admin token on a device’s login page indicates a significant security oversight that could be exploited if not addressed promptly.”
— an anonymous cybersecurity researcher
As an affiliate, we earn on qualifying purchases.
Unresolved Questions About the Device and Exposure
It remains unclear whether the embedded GitHub token was intentionally included by the manufacturer or was an accidental exposure due to a misconfiguration. The extent of potential exploitation and whether other devices are affected are still under investigation. No confirmed reports of malicious activity leveraging this token have emerged yet.
As an affiliate, we earn on qualifying purchases.
Next Steps for Security Monitoring and Response
Security teams at affected organizations should review device firmware and access controls immediately. Manufacturers are expected to issue security advisories or firmware updates to remove or secure embedded tokens. Ongoing monitoring of similar devices and further investigation into supply chain practices are also anticipated to prevent future exposures. Researchers and security firms will continue assessing whether this incident indicates a broader vulnerability trend.
smart security camera for small business
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Key Questions
What is a GitHub admin token?
A GitHub admin token is a credential that grants administrative access to GitHub repositories, often used for automation or integrations. If exposed, it can potentially be exploited to access or modify repositories.
How serious is this security breach?
The severity depends on whether the token was active and accessible to malicious actors. Currently, there is no evidence of exploitation, but the potential risk warrants immediate review and mitigation.
Are other devices likely affected?
It is not yet confirmed if other devices or models contain similar embedded tokens. Manufacturers and security researchers are investigating the scope of the exposure.
What should organizations do now?
Organizations should audit their connected devices for similar vulnerabilities, update firmware if available, and implement strict access controls. Monitoring for unusual activity related to device credentials is also recommended.
Will manufacturers issue a fix?
Manufacturers are expected to release security patches or advisories to address the issue, but timelines are not yet confirmed. Security teams should stay alert for official updates.
Source: IdeaNavigator AI
Fall Picks
fall essentials
As an affiliate, we earn on qualifying purchases.